
An Agentic SOC with sovereign AI.
Ciberia brings threat intelligence, threat hunting, Ciberia MDR, an Agentic SOC 24x7 that detects and responds, and exposure monitoring into a single platform. It integrates with your technology and processes data in Spain.
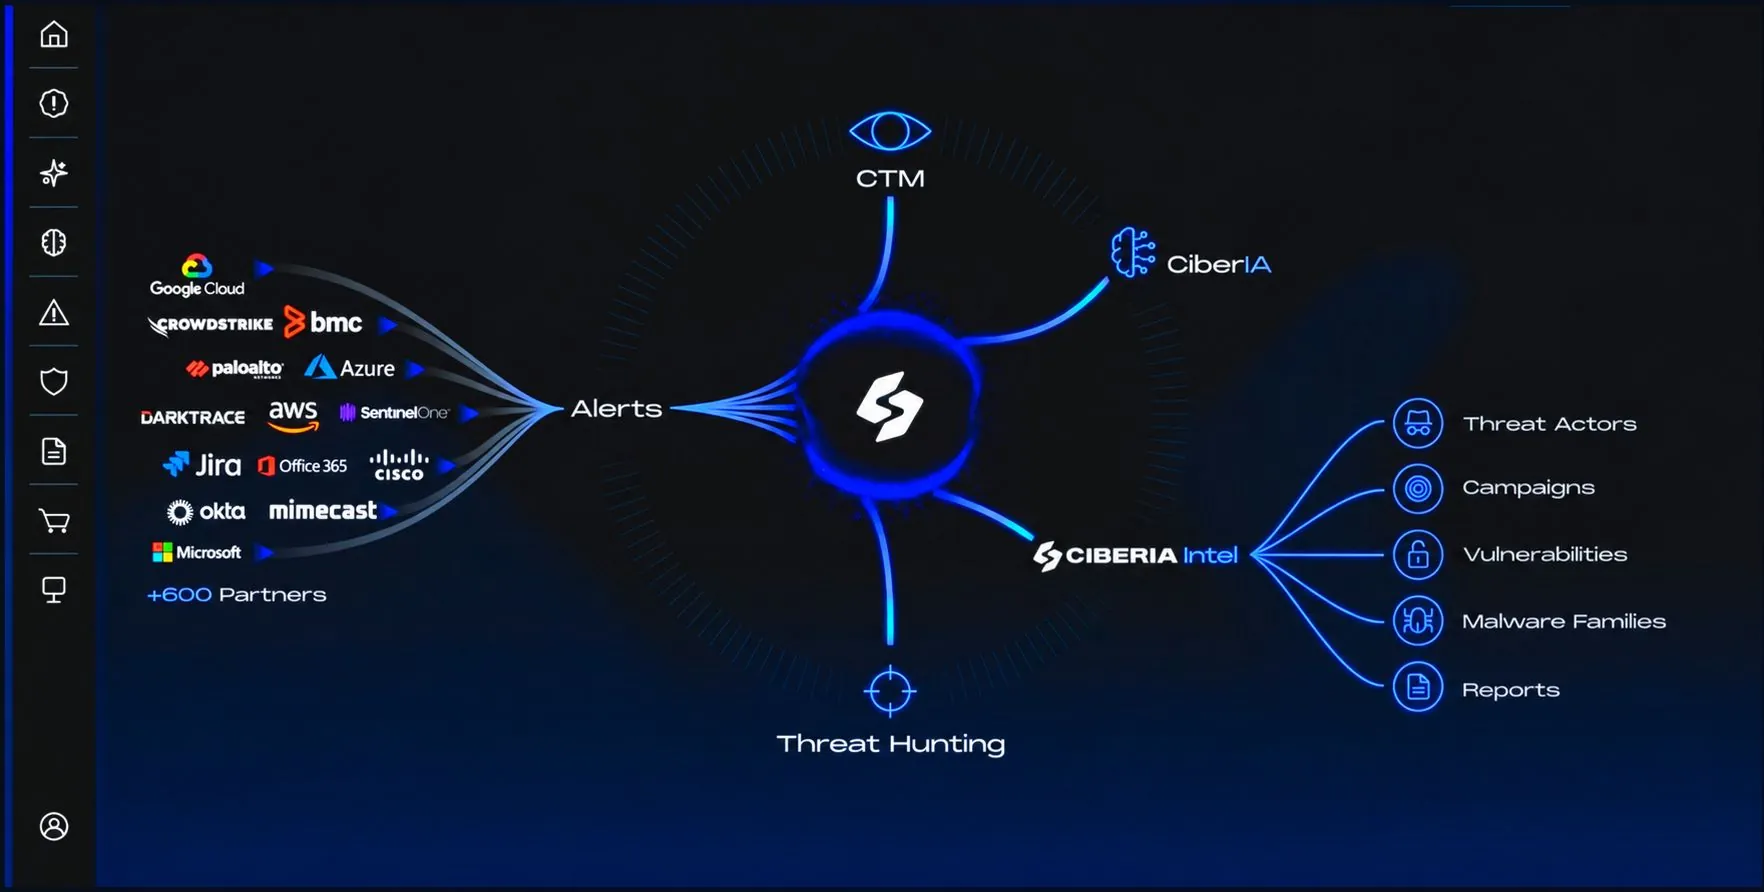
Four products, the same data.
- Ciberia IntelThreat intelligenceThreat actors, campaigns, malware families, vulnerabilities, IOCs and reports, from our own intelligence and third-party sources.
- Threat HuntingProactive huntingOur agentic system looks for what is already inside and has not triggered any alert, with hypotheses based on MITRE ATT&CK.
- Ciberia MDRAgentic SOC 24x7Proprietary AI agents investigate every alert from endpoint, network, email, identity and cloud, and an analyst validates every response.
- Ciberia CTMCredentials, infostealers and dark webLeaked credentials, infostealers, the dark web and forums: what circulates about your organization outside your network.
CiberIA: the AI that handles triage.
90% of triage is automated with our own AI agents. An analyst validates every decision with impact, and all of them are logged.
- Step 1
Alert
Real-time detection across multiple sources.
- Step 2
Context
Our own intelligence, users, assets and correlated cases.
- Step 3
Decision
The AI prioritizes and proposes. The analyst validates. 100% auditable.
- Step 4
Action
Orchestrated response, with a 15-minute SLA for critical alerts.
Works with all your technology.
Ciberia brings together telemetry from more than 600 sources. Processing and models stay on our own infrastructure in Spain.
- Endpoint
- Event collection and log correlation.
- EDR and XDR such as CrowdStrike or SentinelOne
- Impersonation, BEC, malicious attachments and URLs.
- Gateways such as Mimecast or Proofpoint
- Identity
- Anomalous sign-ins and compromised accounts.
- IAM, MFA and directory: Okta, Microsoft, Google
- Network and cloud
- Network anomalies, exfiltration and cloud risk.
- Firewall, NDR and CSPM: Palo Alto, Fortinet, AWS, Azure, Google Cloud
- Threat intelligence
- Validation and reputation of IOCs, campaigns and threat actors.
- Ciberia Intel and third-party sources
- Cases and response
- Correlation of alerts, users and devices. Playbooks, tickets and reports.
- SIEM, SOAR and ITSM
Frequently asked questions
What is an Agentic SOC?
It is a security operations center where AI agents do the repetitive work of triage: they receive the alert, enrich it with context, prioritize it and propose a response. Analysts supervise and validate the decisions that matter.
What does sovereign AI mean?
It means the models and the data stay under control. Ciberia's AI is built on our own architecture, runs on servers located in Spain and does not send your information to third-party LLMs.
Which security certifications does Ciberia hold?
Ciberia holds the certification of conformity with Spain's National Security Framework (ENS) in the High category, the most demanding level of the framework, and ISO/IEC 27001 certification for its information security management system. Data is processed on servers located in Spain and every automatic action is logged.
How long does it take to get Ciberia up and running?
Very little. You are onboarded in under 24 hours and fully deployed within a week, with the Ciberia team supporting you throughout.

Let's talk about your security.
We show you the platform with your technology in mind and look at what we can automate from day one.